
Hack Hard. Hack Fair.
Nepal Cyber Shield 2026 is a Capture The Flag (CTF) competition designed to provide a controlled, authorized, and educational environment where participants can demonstrate practical cybersecurity skills.
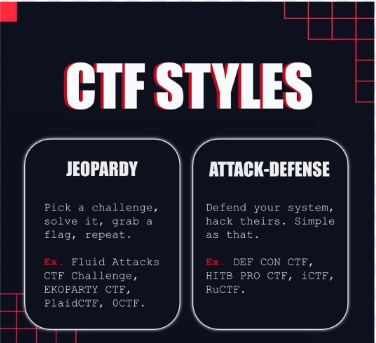
Competition Format
Two Stages. One Cybersecurity Challenge.
01 — Online Qualifier
- Jeopardy-Style CTF
- Participants solve independent cybersecurity challenges and submit flags through the official competition platform.
- The qualifier is designed to test knowledge, creativity, technical skills, and problem-solving across multiple cybersecurity domains.
02 — Physical Round
- King of the Hill
- The Top 10 teams from the Qualifier Round advance to the Physical Round.
- The Physical Round introduces a hands-on competitive environment, with additional round-specific rules and activities announced by the organizers.
Scoring & Submissions
A flag is the challenge-specific value that proves successful completion of a challenge.
Participants must submit flags through the official competition platform unless otherwise instructed.
Challenge scoring may vary according to the competition’s scoring methodology.
Invalid submissions may receive no points, and flags obtained through unauthorized activity or prohibited collaboration may be invalidated.
AUTHORIZED TARGETS ONLY
Stay Inside the Scope
NCS provides authorization only for explicitly designated competition targets.
Participants may interact with systems, services, applications, networks, files, containers, virtual machines, and other resources specifically identified as part of the competition.
The following are not authorized unless explicitly designated as a competition target:
Government systems • Banking & Financial Systems • Payment Platforms • Telecom Infrastructure • Universities • Corporate Services • Personal Systems • Public Internet Infrastructure • Third-Party Cloud Services • Unrelated Domains & IPs
Finding a vulnerability in a real-world system outside the competition does not authorize you to exploit it.
Prohibited Activities
The following activities are strictly prohibited unless a challenge explicitly requires and authorizes the technique:
→ DoS / DDoS attacks
→ Attacking or disrupting the competition platform
→ Attacking the scoreboard
→ Attacking other teams
→ Unauthorized access to team accounts or data
→ Destructive or disruptive activity
→ Malware or destructive payloads outside challenge requirements
→ Persistence outside the intended challenge
→ Social engineering or phishing
→ Unauthorized third-party infrastructure attacks
Participants are responsible for ensuring that their activity remains within the authorized competition scope.